Hardening OPNsense in a homelab: the paths I almost missed
A firewall ruleset can look tidy in the web interface and still allow paths you never intended. I found two while reviewing Nexus, the OPNsense gateway of my Proxmox homelab, Titan.
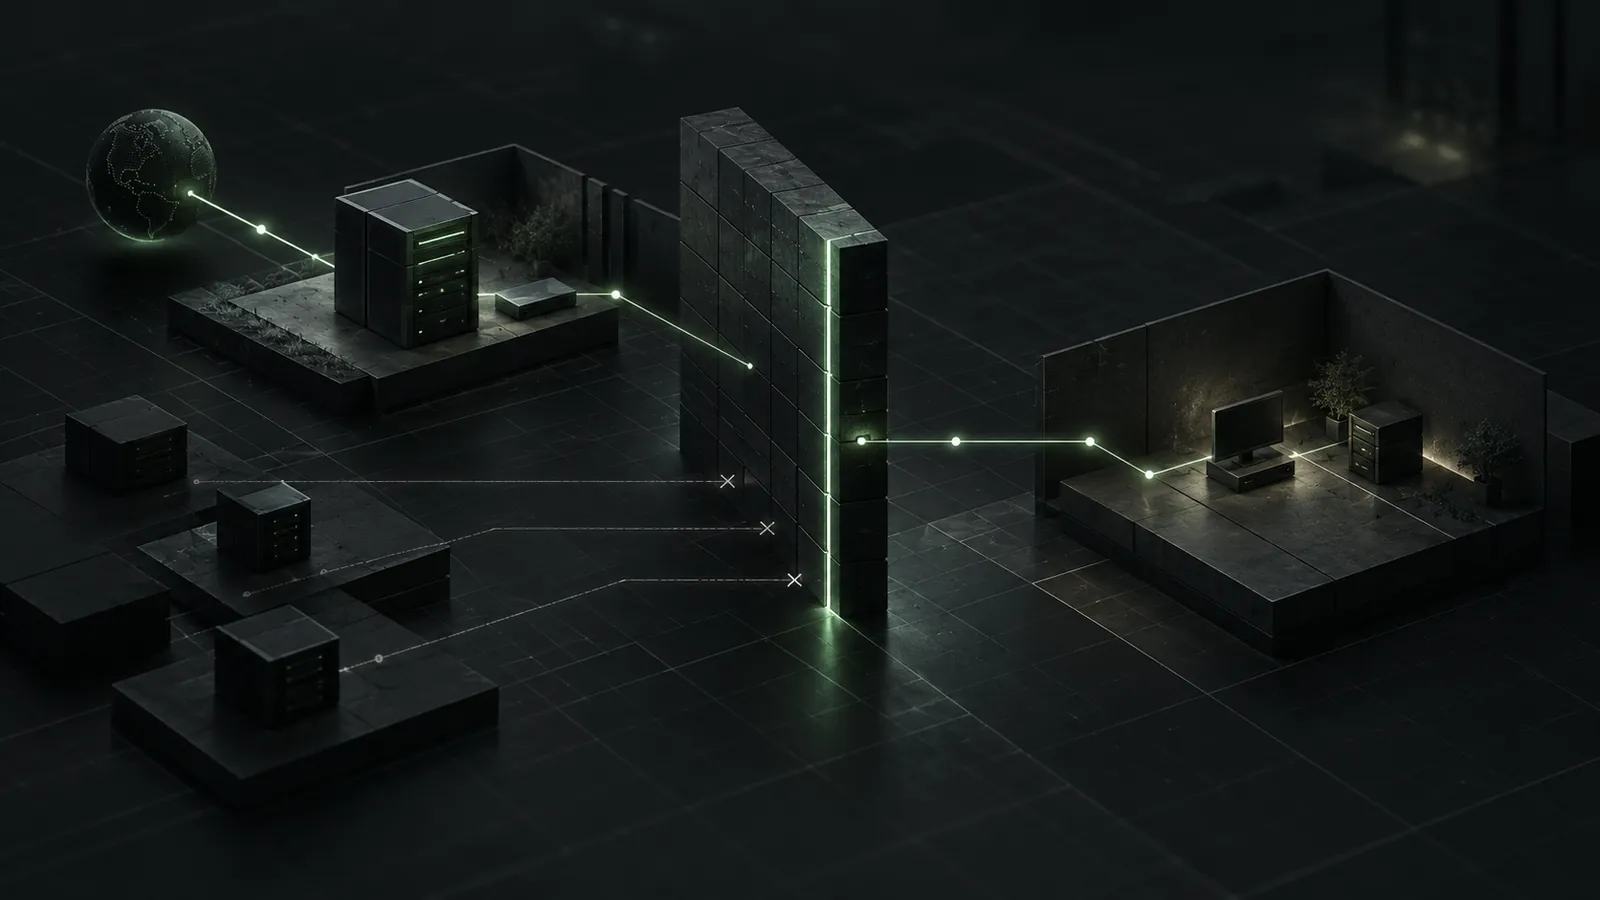
The lab has an internal LAN, a WireGuard network for administration, and a DMZ with Pulsar, a small public web server. I had blocked DMZ → LAN and assumed Pulsar could not reach anything sensitive. It could: the firewall’s own web interface and my admin machine on the VPN were not part of the LAN alias, and a later DMZ → any rule let the traffic through.
These are the commands I used to find and close those paths. Addresses are replaced with placeholders.
Read what PF actually loaded
The GUI shows intent; pfctl shows what is enforced. From the firewall shell:
pfctl -s rules | grep vtnet2
sockstat -4 -l | grep -E 'lighttpd|sshd'
block drop in log quick on vtnet2 inet from (vtnet2:network) to <LAN_NET>
pass in log quick on vtnet2 inet from (vtnet2:network) to any flags S/SA keep state

root  lighttpd  tcp4  *:443
root  lighttpd  tcp4  *:80
root  sshd      tcp4  <fw-lan-ip>:<ssh-port>
That was the whole problem in five lines: the only DMZ block covered the LAN, and the web interface listened on every interface.
Test from the machine you are worried about
From Pulsar, with plain bash:
tcp() { timeout 5 bash -c "echo > /dev/tcp/$1/$2" && echo "open   $1:$2" || echo "closed $1:$2"; }
tcp <fw-dmz-ip> 443       # firewall web UI via the DMZ gateway
tcp <wan-ip> 443          # same UI via the WAN address
ping -c1 -W3 <admin-pc>   # admin machine on WireGuard
All three answered. Every “must fail” test gets a “must work” counterpart — DNS, outbound HTTPS, the site from the Internet — and I ran both after each change.
Close the DMZ
Backup first, and know the way back in. For me that is the VM console on Proxmox.
cp -p /conf/config.xml /conf/backup/config-pre-change-$(date +%Y%m%d%H%M%S).xml
Then, in this order on the DMZ interface (rule evaluation):
- pass DMZ → firewall, port 53 (the firewall is the DMZ’s resolver);
- block DMZ → This Firewall;
- block DMZ →
PRIVATE_NETS, an alias with all RFC1918 ranges, which also covers the VPN; - keep the outbound pass below.
I also bound the web interface to the LAN only. The same tests from Pulsar afterwards:
DNS via firewall            ok
Internet :443               ok
firewall web UI (DMZ/WAN)   closed
admin PC on WireGuard       closed
Anti-lockout was a wider door than it looked
On the LAN, anti-lockout allowed the web UI and SSH from any host, and a generic LAN → any would have allowed it anyway. Before closing it, I checked who actually used it:
grep <anti-lockout-label> /var/log/filter/*.log \
  | grep -oE '[0-9.]+,<fw-lan-ip>,' | sort | uniq -c
2787 <hypervisor>,<fw-lan-ip>,
Only the hypervisor, my SSH jump fallback. So: an explicit pass from the hypervisor to the management ports, a block from the rest of the LAN, a block from the LAN to the VPN network, then anti-lockout disabled. Its rules are evaluated before yours, so the block does nothing until it is off.
One slip: I switched off SSH lockout at the same time by mistake. Similar names, different protection. I restored it and checked it was loaded again:
pfctl -s rules | grep sshlockout
block drop in log quick proto tcp from <sshlockout> to (self) port = <ssh-port>
block drop in log quick proto tcp from <sshlockout> to (self) port = https
Supporting controls on the public web rule
Spamhaus DROP as a URL table alias, blocked on WAN ahead of every pass rule, and a per-source connection limit on the web rule:
pfctl -t SPAMHAUS_DROP -T show | wc -l
pfctl -t SPAMHAUS_DROP -T test 1.10.16.1
pfctl -s rules | grep 'PULSAR_DMZ> port = https'
1710
1/1 addresses match.
pass in log quick on vtnet0 ... to <PULSAR_DMZ> port = https flags S/SA keep state
  (source-track rule, max-src-conn 100, max-src-conn-rate 60/10, overload <virusprot> flush global)
The URL table stayed empty until the aliases were reloaded, so check the count, not the save message. Sources over the limit land in virusprot, which OPNsense already blocks and expires after about an hour. If you lock yourself out while testing:
pfctl -t virusprot -T delete <your-ip>
Both cut noise. Neither is the boundary.
The habit that mattered: for each boundary, write one flow that must work and one that must fail, and test both from the machines involved. “The site still loads” is not “the lab is isolated”.